LOCAL FACEBOOK USERS WARNED ABOUT SNEAKY IN-APP BROWSER ‘SCAREWARE’ SCAM
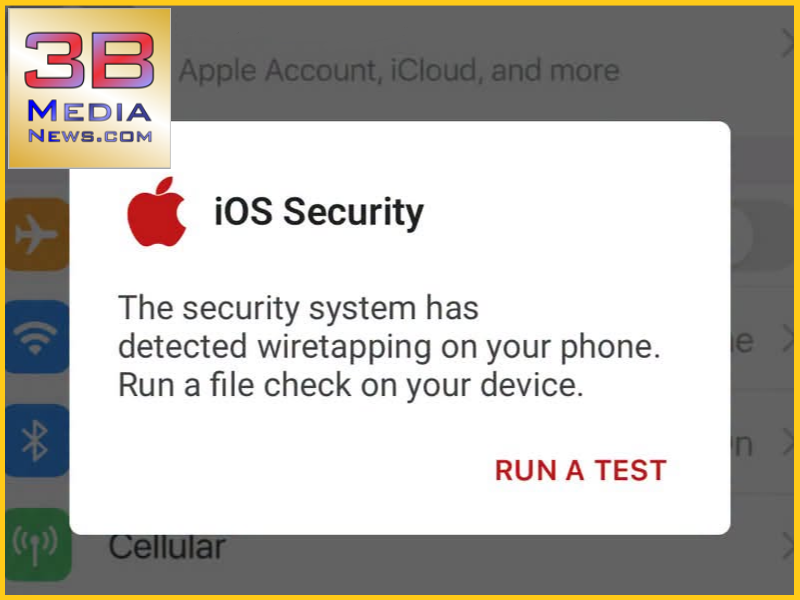
Crossville residents scrolling through local Facebook groups are encountering a deceptive online scam that mimics official smartphone security alerts. Cybersecurity experts and community reports confirm that the tactic relies on malicious advertisements—known as malvertising—purchased through third-party ad networks. When users click on legitimate links inside the Facebook app, these ads hijack the built-in browser to display alarming, fake pop-ups claiming the device is wiretapped or compromised.
Because scammers constantly rotate URLs across domains like threatradar.wiki, recoverwave.live, and safenetgroup.site, the tactic rarely triggers mainstream news coverage, though consumer safety agencies and firms like Surfshark track it extensively.
Security analysts note that spotting the fraud comes down to a few key visual clues:
-
The Address Bar: Real operating system alerts never originate inside a web browser, but the scam pages clearly display third-party URLs at the top.
-
Mismatched Clocks: The fake background settings menu often displays a static time (such as 9:41) that conflicts with the phone’s actual status bar.
-
False Claims: Apple Support explicitly confirms that the company never sends browser pop-ups warning of wiretapping or prompting users to run interactive diagnostics.
Anyone who encounters the pop-up should simply close the browser window or swipe the app closed immediately without tapping any buttons.